 Start a risk review
COMPLETE ENTERPRISE RISK MANAGEMENT
Run the whole risk program.
See beyond the register.
Risk.blue manages known risk from identification through reporting—and detects the unknown, unowned, or out-of-control exposure that red, yellow, and green cannot show.
Bring the exposure into ownership, establish monitoring, and make the response accountable.
THE BLUE LAYER
Red, yellow, and green classify known risk. Blue reveals what the organization cannot yet see, measure, own, or control.
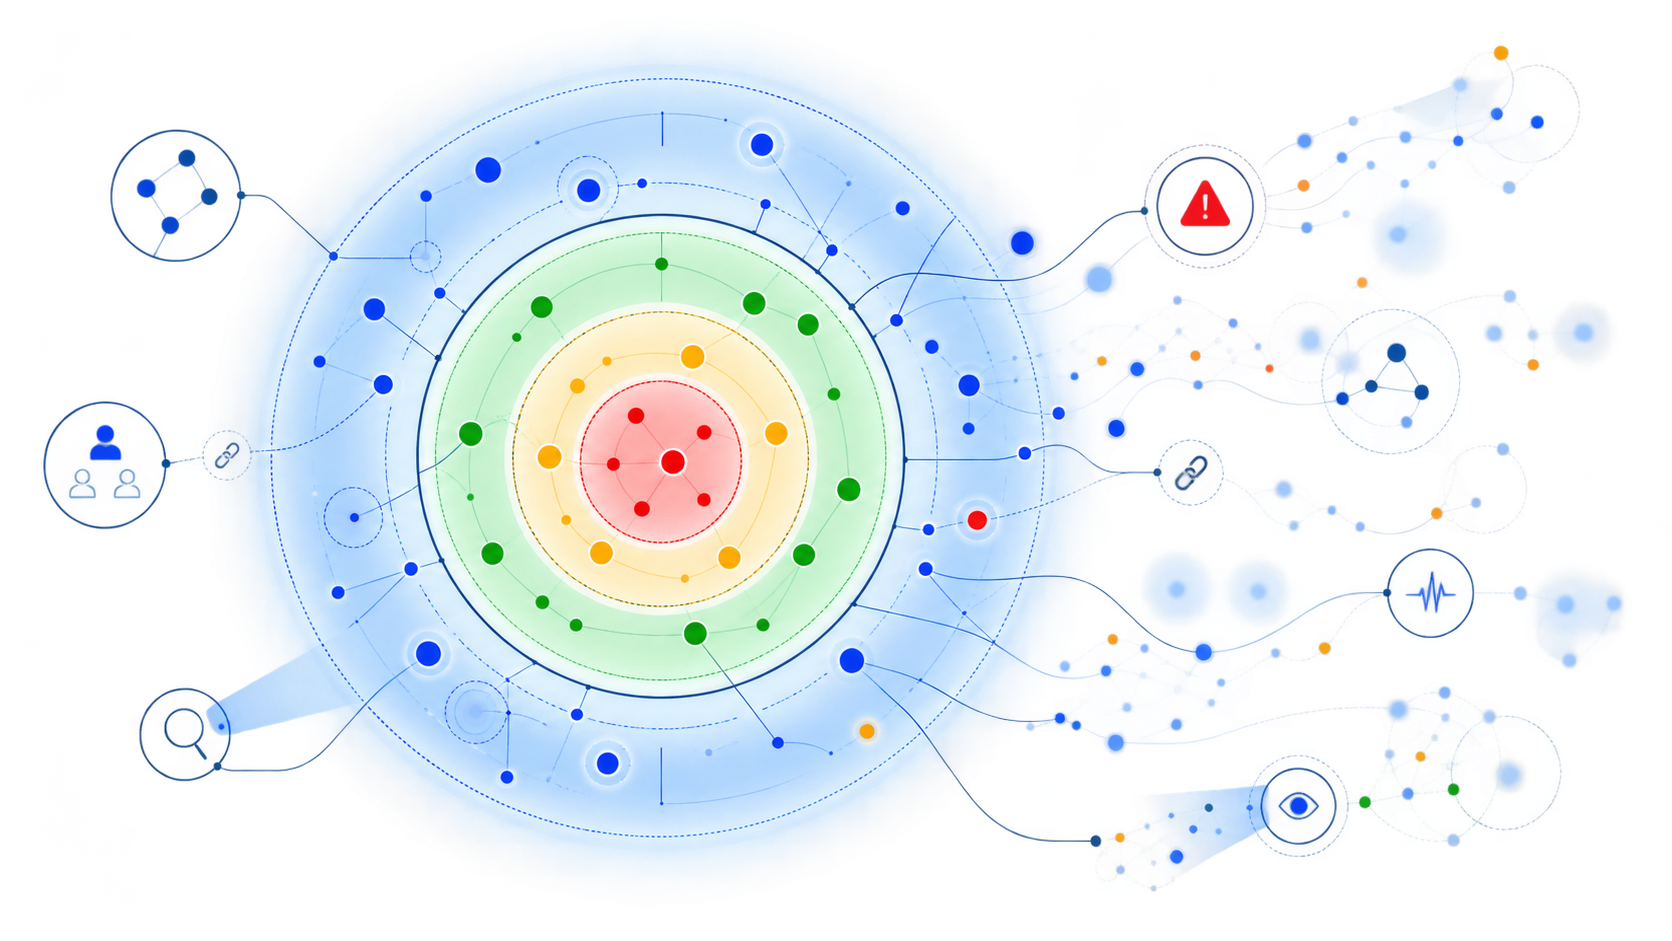
The complete suite runs the risk program. The blue layer continuously looks beyond it—finding weak signals, missing ownership, silent control failures, unmonitored dependencies, and exposure that has not reached the register.
Every discovery becomes an accountable risk: linked to consequences, owners, controls, evidence, thresholds, decisions, and continuous monitoring.
ENTERPRISE RISK DOMAINS
Every risk sector. One operating system.
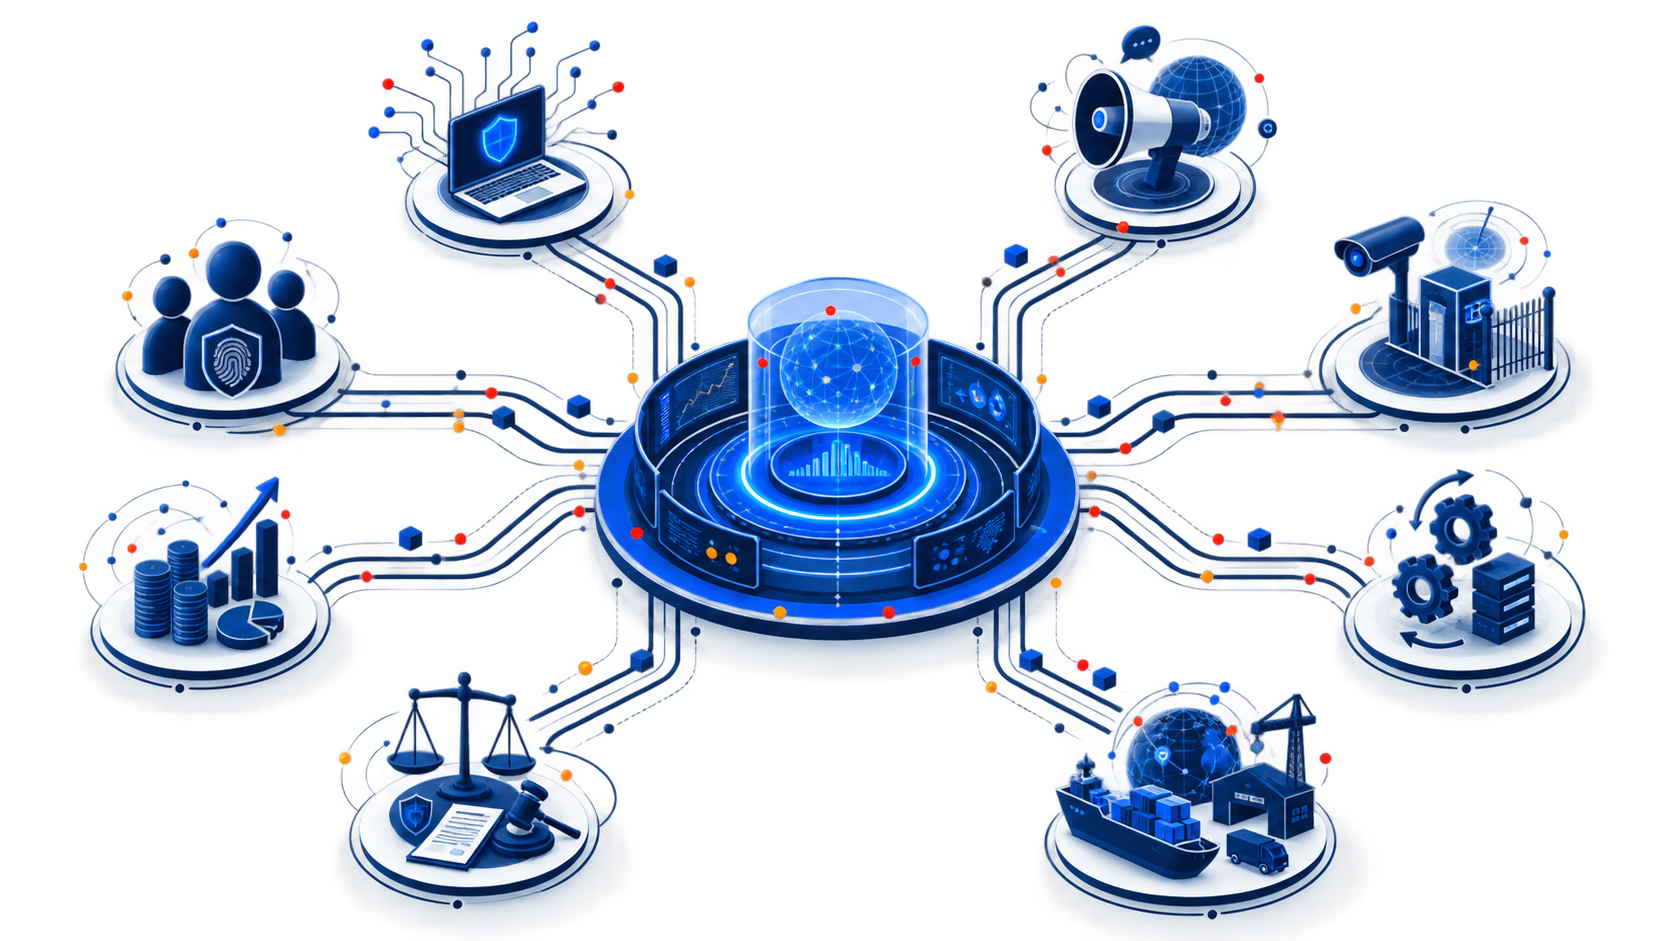
Technology & data risk
Manage technology, cloud, data, AI, applications, infrastructure, and vendor exposure as business risk. Cybersecurity testing and operations are assigned to cyrus.red.
Brand & reputation
Monitor impersonation, public signals, stakeholder trust, narrative shifts, and the reputational effects of operating events.
Physical security
Connect people, facilities, travel, assets, access, environmental threats, and emergency readiness.
Operational resilience
Map critical services, dependencies, capacity, continuity, incident response, recovery, and lessons learned.
Third-party & supply chain
Assess concentration, dependency, control, contractual, geopolitical, and continuity exposure across the extended enterprise.
Legal & regulatory
Track obligations, disputes, regulatory change, evidence, accountability, and emerging compliance exposure.
Financial & commercial
Govern liquidity, credit, fraud, pricing, insurance, contracts, investment, and performance uncertainty.
People & insider risk
Understand workforce capacity, conduct, safety, succession, privileged access, insider threats, and organizational change.
SPECIALIST AGENTIC SERVICES
The risk profile routes work to the people and agents built for it.
Risk.blue maintains the company’s consolidated exposure, ownership, treatment, and residual risk. Independent specialist companies perform bounded industry work and return attributable evidence to the profile.
COSO-DERIVED OPERATING LAYERS